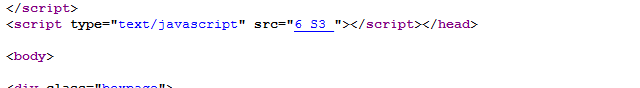
I've noticed recently there is a javascript tag generated in html code only while viewing page

<script type="text/javascript" src="6_S3_"></script>

search for it in file but couldn't find it, and am worried about this.

Dani AI

Generated

Short diagnosis and what to try first

If the same unexpected script shows up in View Source on several different office PCs but not from home, the modification is almost certainly happening before the browser runs page JavaScript — i.e., on the office network (transparent proxy / gateway / ISP) or a centralized security product — rather than being added by each browser or by your server-side files. That explains why ’s suggestion about extensions is useful to check, but unlikely when every machine and OS at the office shows the same injected tag; and ’s local copy test is a good sanity check for your server files. (stackoverflow.com)

Concrete checks you can run (quick, non-destructive)

Save the raw HTTP response from an office machine and inspect it outside the browser so you’re looking at exactly what arrived over the wire. Example workflow:

# fetch raw response to a file
curl -sS -o /tmp/page.html 'https://your-site.example'

# search the file for the string you saw in view-source
grep -n 'pattern-you-saw' /tmp/page.html || echo 'not found'

Also open DevTools → Network → click the document request → Response to see the raw server response there. If the recorded file or the Network response contains the injected code, the change happened in transit. (man.archlinux.org)

Likely causes and how to distinguish them

  • Network/proxy insertion (ad injection, captive portals, web gateways) — documented real-world examples exist where ISPs or gateways add JS to pages.
  • Enterprise HTTPS inspection / TLS interception: when a proxy terminates/re-encrypts HTTPS it can alter content; check the page certificate’s Issuer on an affected machine — a corporate appliance CA is a strong signal of TLS interception.
    If the injected code is present in the raw response, raise it with your network/IT team (don’t remove trust roots yourself on managed machines). (arstechnica.com)

If the raw response is clean

If curl/Network shows no injection, the problem is local: browser extension, an AV/web-filtering tool, or malware on those office machines. Test with a clean browser profile or a temporary portable browser, disable extensions, and run up-to-date anti-malware scans. On Windows you can also check system proxy settings (netsh winhttp show proxy) to spot centrally-configured proxies. If the issue persists across machines and networks, involve your IT/security team for an appliance-level investigation. (learn.microsoft.com)

Recommended Answers

All 10 Replies

Copy all files to localhost and check if there is same behaviour.

Sorry my magic ball is in the shop for repairs, so please at least try to give us a clue to what you're on about.

How do you mean generated? Have you saved a HTML file and you've opened it in a browser and found that? Are you certain it's not in the HTML file? Do you see it in all browsers? ...

What tools are you using to generate your PHP? This doesn't happen "auto-magically".

I see this code only when view source the page, and noticed, not only in my pages , a lot of websites have this code , so I think this generated by some tools installed on office PC, I opened site from my home and saw there is no javascript generated.
thanks for help, but I really need to know which programs cause this.

It's probably just an adblocker or another browser extension that is changing the markup.

Member Avatar for Member #120589

WHen you say "view source the page" do you mean traditional "view source" or viewing the source as in Chrome's "Inspect Element > Elements". The latter will give you an updated DOM after all javascript scripts have been run and may include scripts from browser plugins. Are you using any third party scripts?

@diafol I meant by pressing CTRL+U
but as I told you before its only in Office PC maybe there is some of programs or extension cause this.

Member Avatar for Member #120589

OK, so traditional view source. Are you using the same browser at home and in the office? It may be down to privacy settings set by your workplace. Strange this particular src not documented though.

now am at office and tried different PCs with different OS and all are the same code generated
jsjs.png

This is virus. You must on hands to remove js code. And pray not appear

Be a part of the DaniWeb community

We're a friendly, industry-focused community of developers, IT pros, digital marketers, and technology enthusiasts meeting, networking, learning, and sharing knowledge.