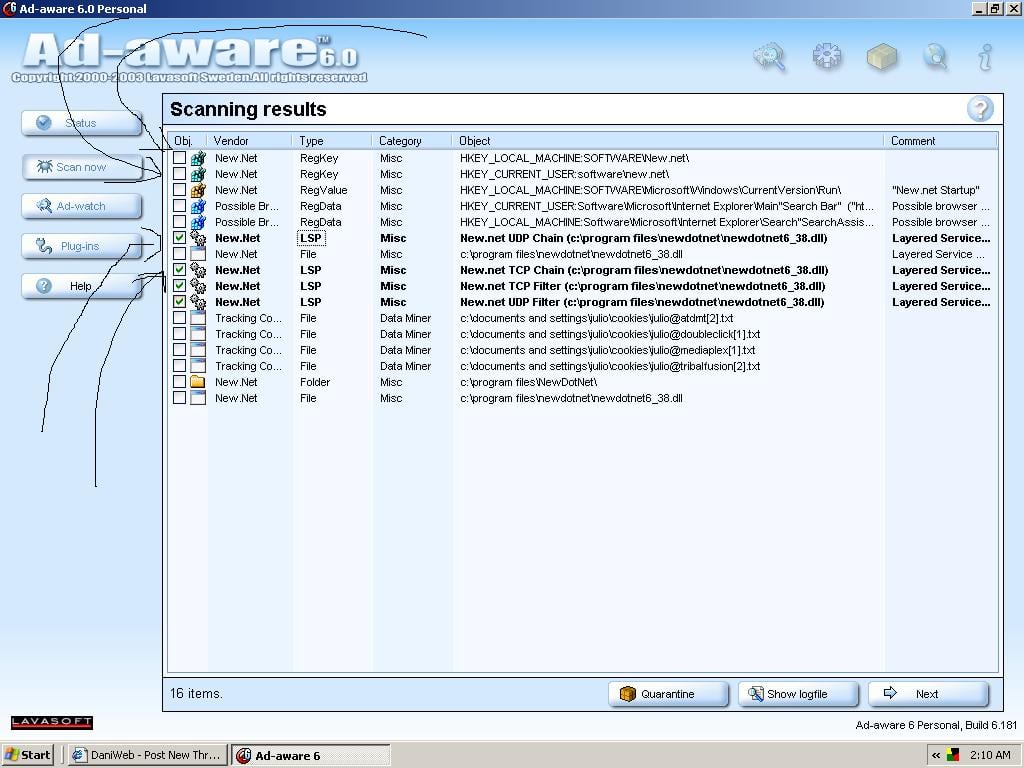
Hey, my adware keeps picking this new.net thing i cant seem to get rid off.. after scanning my drive adware tells me i couldnt get rid of those Net. files and to reboot my computer to do so... but that doesn work either..
I dont have have zone alarm installed with this computer though, cos its a major cpu feeder.. maybe might have too after this event,thanks..


my antivurs apps
adware 6
Avg 6.0
Spy Bot
HiJack This

heres my Hijack Log

Logfile of HijackThis v1.97.7
Scan saved at 2:07:55 AM, on 12/8/2004
Platform: Windows XP SP2 (WinNT 5.01.2600)
MSIE: Internet Explorer v6.00 SP2 (6.00.2900.2180)

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\Explorer.EXE
C:\PROGRA~1\Grisoft\AVG6\avgserv.exe
C:\PROGRA~1\Toolbar\TBPSSvc.exe
C:\Program Files\Common Files\WinTools\WToolsA.exe
C:\WINDOWS\system32\CTHELPER.EXE
C:\Program Files\Grisoft\AVG6\avgcc32.exe
C:\Program Files\QuickTime\qttask.exe
C:\Program Files\Common Files\Real\Update_OB\realsched.exe
C:\Program Files\Viewpoint\Viewpoint Manager\ViewMgr.exe
C:\PROGRA~1\Toolbar\TBPS.exe
C:\WINDOWS\system32\rundll32.exe
C:\Program Files\Common Files\WinTools\WToolsS.exe
C:\Program Files\Common Files\WinTools\WSup.exe
C:\PROGRA~1\Toolbar\PIB.exe
C:\Program Files\Internet Explorer\iexplore.exe
C:\Program Files\Lavasoft\Ad-aware 6\Ad-aware.exe
C:\WINDOWS\System32\svchost.exe
C:\DOCUME~1\julio\LOCALS~1\Temp\Temporary Directory 1 for hijackthis.zip\HijackThis.exe

R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Bar =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,SearchAssistant =
R3 - URLSearchHook: (no name) - {87766247-311C-43B4-8499-3D5FEC94A183} - C:\PROGRA~1\COMMON~1\WinTools\WToolsB.dll
O2 - BHO: (no name) - {4E7BD74F-2B8D-469E-C0FF-FD60B590A87D} - C:\PROGRA~1\COMMON~1\Real\Toolbar\realbar.dll
O2 - BHO: (no name) - {53707962-6F74-2D53-2644-206D7942484F} - C:\Program Files\Spybot - Search & Destroy\SDHelper.dll
O2 - BHO: (no name) - {87766247-311C-43B4-8499-3D5FEC94A183} - C:\PROGRA~1\COMMON~1\WinTools\WToolsB.dll
O3 - Toolbar: REALBAR - {4E7BD74F-2B8D-469E-C0FF-FD60B590A87D} - C:\PROGRA~1\COMMON~1\Real\Toolbar\realbar.dll
O4 - HKLM\..\Run: [CTHelper] CTHELPER.EXE
O4 - HKLM\..\Run: [AVG_CC] C:\Program Files\Grisoft\AVG6\avgcc32.exe /startup
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKLM\..\Run: [TkBellExe] "C:\Program Files\Common Files\Real\Update_OB\realsched.exe" -osboot
O4 - HKLM\..\Run: [ViewMgr] C:\Program Files\Viewpoint\Viewpoint Manager\ViewMgr.exe
O4 - HKLM\..\Run: [WinTools] C:\Program Files\Common Files\WinTools\WToolsA.exe
O4 - HKLM\..\Run: [webHancer Survey Companion] "C:\Program Files\webHancer\Programs\whSurvey.exe"
O4 - HKLM\..\Run: [TBPS] C:\PROGRA~1\Toolbar\TBPS.exe
O4 - HKLM\..\Run: [MSConfig] C:\WINDOWS\PCHealth\HelpCtr\Binaries\MSConfig.exe /auto
O4 - HKLM\..\Run: [New.net Startup] rundll32 C:\PROGRA~1\NEWDOT~1\NEWDOT~2.DLL,NewDotNetStartup -s
O4 - HKLM\..\RunOnce: [WinTools] C:\PROGRA~1\COMMON~1\WinTools\WToolsA.exe /boot
O9 - Extra button: AIM (HKLM)
O9 - Extra button: Messenger (HKLM)
O9 - Extra 'Tools' menuitem: Windows Messenger (HKLM)
O10 - Hijacked Internet access by New.Net
O16 - DPF: DigiChat Applet -
O16 - DPF: {02BF25D5-8C17-4B23-BC80-D3488ABDDC6B} (QuickTime Object) - http://www.apple.com/qtactivex/qtplugin.cab
O16 - DPF: {0E5F0222-96B9-11D3-8997-00104BD12D94} (PCPitstop Utility) -
O16 - DPF: {1842B0EE-B597-11D4-8997-00104BD12D94} (iCC Class) -
O16 - DPF: {1C78AB3F-A857-482E-80C0-3A1E5238A565} - file://C:\install.cab
O16 - DPF: {3334504D-9980-0010-8000-00AA00389B71} -
O16 - DPF: {33564D57-0000-0010-8000-00AA00389B71} -
O16 - DPF: {56336BCB-3D8A-11D6-A00B-0050DA18DE71} (RdxIE Class) -
O16 - DPF: {65E7DB1D-0101-4100-BD66-C5C78C917F93} -
O16 - DPF: {90C9629E-CD32-11D3-BBFB-00105A1F0D68} (InstallShield International Setup Player) -
O16 - DPF: {9F1C11AA-197B-4942-BA54-47A8489BB47F} -
O16 - DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} (Shockwave Flash Object) - http://download.macromedia.com/pub/shockwave/cabs/flash/swflash.cab
O16 - DPF: {FA3662C3-B8E8-11D6-A667-0010B556D978} (IWinAmpActiveX Class) -
Dani AI

Generated

Good progress — ’s logs show NewDotNet, the WebSearch/toolbar bits and WinTools mostly handled thanks to the steps from and . The remaining work is about cleaning hidden persistence (network hooks, orphaned services/tasks, restore points) and preventing reinfection when files are copied to the other PC.

Final-clean checklist (do these before declaring the machine clean)

  • Repair the network stack (NewDotNet commonly leaves a broken Winsock/LSP chain). From an elevated command prompt run, then reboot:
netsh winsock reset
netsh int ip reset resetlog.txt
  • Remove leftover services/tasks that show “file missing” or that keep reinstalling the toolbar. Confirm the service’s short name in Services.msc, then remove if needed from an elevated prompt:
sc delete "ServiceShortName"

Always confirm the exact service name first and back up the registry or create a temporary restore point before deleting system entries.

  • Check the hosts file (system32\drivers\etc\hosts) for unexpected redirects and clear any malicious lines; check Scheduled Tasks for odd entries and delete them. After confirming the machine is clean, clear old System Restore snapshots (turn System Restore off, reboot, then re-enable) so malware saved in restore points cannot reappear.

  • Do a final set of full scans in Safe Mode (no networking) with updated definitions. Any removable media or files transferred to the music PC should be rescanned before moving. Note ’s point about P2P installers — these can reintroduce adware; avoid bundled installs or choose custom installs to opt out.

If toolbars or hooks reappear after these steps, use an autorun/boot analysis tool to find whatever component is re-registering them; persistent re-infection may be faster to resolve with a repair install or a clean OS reinstall after backing up data. Keep the HJT backup folder until the system has been stable for a while.

Recommended Answers

All 15 Replies

You running hijackthis fro the zip amd ot old version ,do the following ,

,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,
Please do this.
Download 'Hijack This!'. http://www.spywareinfo.com/~merijn/files/HijackThis.exe
Save it in a convenient permanent folder such as C:\HJT\, double click HijackThis.exe, and hit "Scan".

Your copy of HijackThis needs to be in a folder of it's own. When HJT fixes anything, it makes backups of the original files in the folder it is in. Since Temporary folders are emptied now and then (the files are DELETED), it would not be a good idea to have your backups there. Those backups would be VITAL to restoring your system if something went wrong in the FIX process!


1. Please go to you're 'My Documents' folder, right-click and select 'New > Folder' then name the folder 'HJT'.

2. Copy and paste HijackThis.exe to the new folder.

3. Close ALL windows except HJT

4. SCAN with HJT

5. POST the new log in this thread using 'Add Reply'

DO NOT MAKE ANY CHANGES OR CLICK "FIX CHECKED" UNTIL WE CHECK THE LOG, AS SOME OF THE FILES ARE LEGIT AND VITAL TO YOUR COMPUTER'S HEALTH

do this for the 010, new.net .,,,,,,,,,,,,,,,,,,
,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,
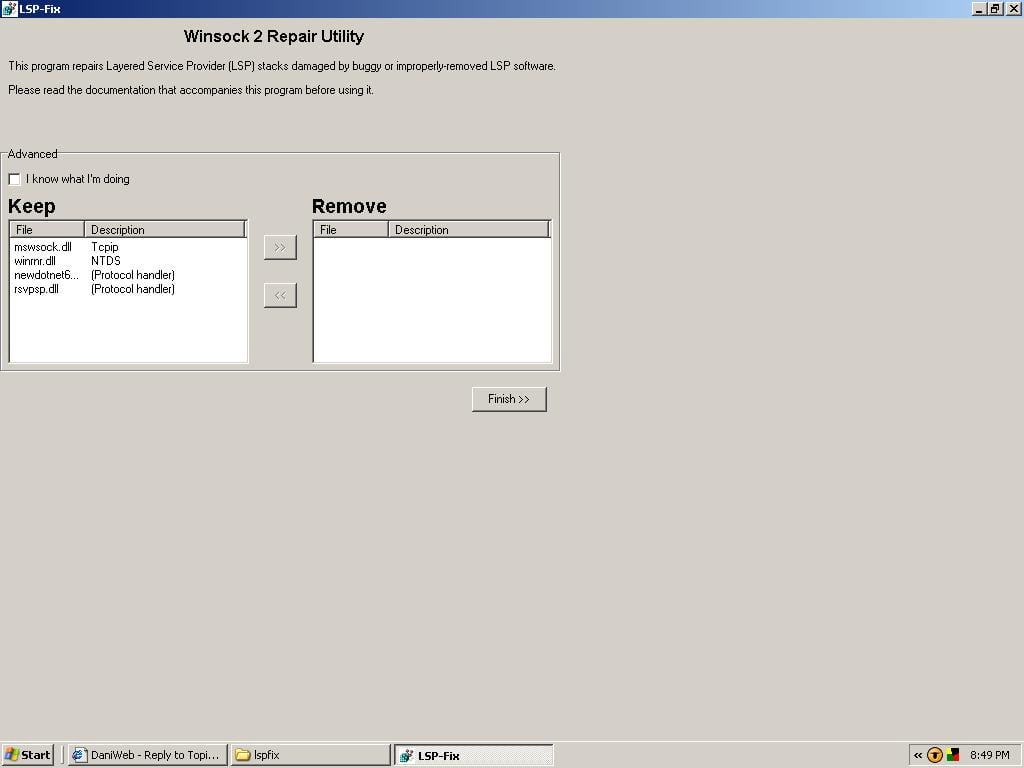
First, download LSPfix here: http://www.cexx.org/lspfix.htm
Launch the application, and click the "I know what I'm doing" checkbox.
Check all instances of New.Net(and nothing else), and move them to the "Remove" pane.
Then click Finish.

,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,
Then run hijack again and post a fresh log

O4 - HKLM\..\Run: [MSConfig] C:\WINDOWS\PCHealth\HelpCtr\Binaries\MSConfig.exe /auto

please open msconfig and set it to normal startup load all sevices and devices ,so we can see the stuff you disabled.

Just adding to Caperjacks reply, Please go here for Wintools removal instructions.

Remove Newdotnet from add/remove programs, or by going and scrolling down to the uninstall tool.

In add\remove programs, also uninstall webHancer.

Thanks Caperjack & Crunchie for helping me out .
Ok before i just booted my computer and before it made it to the desktop..some WebSearch window automatically popped up ,soo i think something else is lurking ..
I downloaded the LSPfix and saw the Netdotnet6_38dll ,under protocal,but soo is this " rsvpsp.dll" just curious what this is ? I havent removed anything in there yet , till i get approval. I posted a jpeg at the bottom

As for the Hijack this , i just want to make sure im doing this right.. I created a new folder and named it HJT in " my documents" and saved the hijackthisexe. in the HJT folder.

I changed my start up to normal now, i was doing selective before cause Of E-donkey would start up everytime and i couldnt disable it in msconfig before..

let me know if everythings is done right ,and ill post a HIjackThis log

rsvpsp.dll is a legitimate system file. The uninstall of Newdotnet should remove the entry from LSPfix.
You seem to have done everything right, so lets see your log. Let us know exactly what you have been able to remove.

Ok the Newdotnet file has been removed .

and heres my new Hijack this log


Logfile of HijackThis v1.98.2
Scan saved at 10:43:26 AM, on 12/9/2004
Platform: Windows XP SP2 (WinNT 5.01.2600)
MSIE: Internet Explorer v6.00 SP2 (6.00.2900.2180)

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\Explorer.EXE
C:\PROGRA~1\Grisoft\AVG6\avgserv.exe
C:\PROGRA~1\Toolbar\TBPSSvc.exe
C:\Program Files\Common Files\WinTools\WToolsA.exe
C:\WINDOWS\system32\CTHELPER.EXE
C:\Program Files\Grisoft\AVG6\avgcc32.exe
C:\Program Files\QuickTime\qttask.exe
C:\Program Files\Common Files\Real\Update_OB\realsched.exe
C:\Program Files\Viewpoint\Viewpoint Manager\ViewMgr.exe
C:\PROGRA~1\Toolbar\TBPS.exe
C:\WINDOWS\system32\rundll32.exe
C:\Program Files\Common Files\WinTools\WSup.exe
C:\PROGRA~1\Toolbar\PIB.exe
C:\Program Files\Common Files\WinTools\WToolsS.exe
C:\Program Files\Internet Explorer\iexplore.exe
C:\Documents and Settings\julio\My Documents\HJT\HijackThis.exe

R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Bar =
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
R3 - URLSearchHook: (no name) - {87766247-311C-43B4-8499-3D5FEC94A183} - C:\PROGRA~1\COMMON~1\WinTools\WToolsB.dll
O2 - BHO: REALBAR - {4E7BD74F-2B8D-469E-C0FF-FD60B590A87D} - C:\PROGRA~1\COMMON~1\Real\Toolbar\realbar.dll
O2 - BHO: (no name) - {53707962-6F74-2D53-2644-206D7942484F} - C:\Program Files\Spybot - Search & Destroy\SDHelper.dll
O2 - BHO: (no name) - {87766247-311C-43B4-8499-3D5FEC94A183} - C:\PROGRA~1\COMMON~1\WinTools\WToolsB.dll
O2 - BHO: (no name) - {8952A998-1E7E-4716-B23D-3DBE03910972} - C:\PROGRA~1\Toolbar\toolbar.dll
O3 - Toolbar: REALBAR - {4E7BD74F-2B8D-469E-C0FF-FD60B590A87D} - C:\PROGRA~1\COMMON~1\Real\Toolbar\realbar.dll
O3 - Toolbar: &Search Toolbar - {339BB23F-A864-48C0-A59F-29EA915965EC} - C:\PROGRA~1\Toolbar\toolbar.dll
O4 - HKLM\..\Run: [CTHelper] CTHELPER.EXE
O4 - HKLM\..\Run: [AVG_CC] C:\Program Files\Grisoft\AVG6\avgcc32.exe /startup
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKLM\..\Run: [TkBellExe] "C:\Program Files\Common Files\Real\Update_OB\realsched.exe" -osboot
O4 - HKLM\..\Run: [ViewMgr] C:\Program Files\Viewpoint\Viewpoint Manager\ViewMgr.exe
O4 - HKLM\..\Run: [WinTools] C:\Program Files\Common Files\WinTools\WToolsA.exe
O4 - HKLM\..\Run: [webHancer Survey Companion] "C:\Program Files\webHancer\Programs\whSurvey.exe"
O4 - HKLM\..\Run: [TBPS] C:\PROGRA~1\Toolbar\TBPS.exe
O4 - HKLM\..\Run: [New.net Startup] rundll32 C:\PROGRA~1\NEWDOT~1\NEWDOT~2.DLL,NewDotNetStartup -s
O4 - HKLM\..\Run: [eDonkey2000] "C:\Program Files\eDonkey2000\eDonkey2000.exe" -t
O4 - HKLM\..\RunOnce: [WinTools] C:\PROGRA~1\COMMON~1\WinTools\WToolsA.exe /boot
O4 - HKCU\..\Run: [WinTools] C:\PROGRA~1\COMMON~1\WinTools\WToolsA.exe
O9 - Extra button: AIM - {AC9E2541-2814-11d5-BC6D-00B0D0A1DE45} - C:\Program Files\AIM\aim.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O10 - Hijacked Internet access by New.Net
O16 - DPF: DigiChat Applet -
O16 - DPF: {0E5F0222-96B9-11D3-8997-00104BD12D94} (PCPitstop Utility) -
O16 - DPF: {1842B0EE-B597-11D4-8997-00104BD12D94} (iCC Class) -
O16 - DPF: {1C78AB3F-A857-482E-80C0-3A1E5238A565} - file://C:\install.cab
O16 - DPF: {56336BCB-3D8A-11D6-A00B-0050DA18DE71} (RdxIE Class) -
O16 - DPF: {65E7DB1D-0101-4100-BD66-C5C78C917F93} -
O16 - DPF: {90C9629E-CD32-11D3-BBFB-00105A1F0D68} (InstallShield International Setup Player) -
O16 - DPF: {FA3662C3-B8E8-11D6-A667-0010B556D978} (IWinAmpActiveX Class) -
O18 - Protocol: tpro - {FF76A5DA-6158-4439-99FF-EDC1B3FE100C} - C:\PROGRA~1\Toolbar\toolbar.dll

Just want to know whats safe to get rid off in here,please .thanks

You need to do what Chrunchie said to do in post #5 ,you still have new.net and WinTools

I followed Crunchies 5th reply and deleted al of wintools in safe mode, but I didnt see a web enhancer or newtdotnet , in my add/romve programs....but theres a websearch tool bar size 3.35mb , websearch tools, and a winstool easy installer by websearch in there ....should i go ahead and delete them in safe mode?

oh and what should i do with the Hijack back up folder , do i get rid of it or jsut keep it where it ?
here my Hijack Log ...thanks again

Logfile of HijackThis v1.98.2
Scan saved at 8:36:44 PM, on 12/13/2004
Platform: Windows XP SP2 (WinNT 5.01.2600)
MSIE: Internet Explorer v6.00 SP2 (6.00.2900.2180)

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\Explorer.EXE
C:\PROGRA~1\Toolbar\TBPS.exe
C:\PROGRA~1\Toolbar\PIB.exe
C:\PROGRA~1\Grisoft\AVG6\avgserv.exe
C:\WINDOWS\system32\CTHELPER.EXE
C:\Program Files\Grisoft\AVG6\avgcc32.exe
C:\Program Files\QuickTime\qttask.exe
C:\Program Files\Common Files\Real\Update_OB\realsched.exe
C:\Program Files\Viewpoint\Viewpoint Manager\ViewMgr.exe
C:\WINDOWS\system32\rundll32.exe
C:\PROGRA~1\Toolbar\TBPSSvc.exe
C:\WINDOWS\system32\wscntfy.exe
C:\Program Files\Internet Explorer\iexplore.exe
C:\Documents and Settings\julio\My Documents\HJT\HijackThis.exe

R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Bar =
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,SearchAssistant =
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,CustomizeSearch = res://C:\PROGRA~1\Toolbar\toolbar.dll/sa
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch = res://C:\PROGRA~1\Toolbar\toolbar.dll/sa
R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
R3 - URLSearchHook: (no name) - {8952A998-1E7E-4716-B23D-3DBE03910972} - C:\PROGRA~1\Toolbar\toolbar.dll
O2 - BHO: REALBAR - {4E7BD74F-2B8D-469E-C0FF-FD60B590A87D} - C:\PROGRA~1\COMMON~1\Real\Toolbar\realbar.dll
O2 - BHO: (no name) - {53707962-6F74-2D53-2644-206D7942484F} - C:\Program Files\Spybot - Search & Destroy\SDHelper.dll
O2 - BHO: (no name) - {8952A998-1E7E-4716-B23D-3DBE03910972} - C:\PROGRA~1\Toolbar\toolbar.dll
O3 - Toolbar: REALBAR - {4E7BD74F-2B8D-469E-C0FF-FD60B590A87D} - C:\PROGRA~1\COMMON~1\Real\Toolbar\realbar.dll
O3 - Toolbar: &Search Toolbar - {339BB23F-A864-48C0-A59F-29EA915965EC} - C:\PROGRA~1\Toolbar\toolbar.dll
O4 - HKLM\..\Run: [CTHelper] CTHELPER.EXE
O4 - HKLM\..\Run: [AVG_CC] C:\Program Files\Grisoft\AVG6\avgcc32.exe /startup
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKLM\..\Run: [TkBellExe] "C:\Program Files\Common Files\Real\Update_OB\realsched.exe" -osboot
O4 - HKLM\..\Run: [ViewMgr] C:\Program Files\Viewpoint\Viewpoint Manager\ViewMgr.exe
O4 - HKLM\..\Run: [webHancer Survey Companion] "C:\Program Files\webHancer\Programs\whSurvey.exe"
O4 - HKLM\..\Run: [TBPS] C:\PROGRA~1\Toolbar\TBPS.exe
O4 - HKLM\..\Run: [New.net Startup] rundll32 C:\PROGRA~1\NEWDOT~1\NEWDOT~2.DLL,NewDotNetStartup -s
O4 - HKLM\..\Run: [eDonkey2000] "C:\Program Files\eDonkey2000\eDonkey2000.exe" -t
O9 - Extra button: AIM - {AC9E2541-2814-11d5-BC6D-00B0D0A1DE45} - C:\Program Files\AIM\aim.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O10 - Hijacked Internet access by New.Net
O16 - DPF: DigiChat Applet -
O16 - DPF: {0E5F0222-96B9-11D3-8997-00104BD12D94} (PCPitstop Utility) -
O16 - DPF: {1842B0EE-B597-11D4-8997-00104BD12D94} (iCC Class) -
O16 - DPF: {1C78AB3F-A857-482E-80C0-3A1E5238A565} - file://C:\install.cab
O16 - DPF: {56336BCB-3D8A-11D6-A00B-0050DA18DE71} (RdxIE Class) -
O16 - DPF: {65E7DB1D-0101-4100-BD66-C5C78C917F93} -
O16 - DPF: {90C9629E-CD32-11D3-BBFB-00105A1F0D68} (InstallShield International Setup Player) -
O16 - DPF: {FA3662C3-B8E8-11D6-A667-0010B556D978} (IWinAmpActiveX Class) -
O18 - Protocol: tpro - {FF76A5DA-6158-4439-99FF-EDC1B3FE100C} - C:\PROGRA~1\Toolbar\toolbar.dll

Check in add\remove for all those mentioned as it is better to uninstall, if possible.
Did you try the uninstall tool from the link I gave you for New.net?

Keep the HJT backup folder for now.

Open Task Manager & end process on the following:
TBPS.exe
PIB.exe

Go to C:\PROGRAM FILES and delete the Toolbar folder.

Scan with hijackthis and tick the boxes next to all the following entries, then close all browser and explorer windows, and hit the "Fix checked" button.

R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Bar =
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,SearchAssistant =
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,CustomizeSearch = res://C:\PROGRA~1\Toolbar\toolbar.dll/sa
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch = res://C:\PROGRA~1\Toolbar\toolbar.dll/sa
R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
R3 - URLSearchHook: (no name) - {8952A998-1E7E-4716-B23D-3DBE03910972} - C:\PROGRA~1\Toolbar\toolbar.dll

O2 - BHO: (no name) - {8952A998-1E7E-4716-B23D-3DBE03910972} - C:\PROGRA~1\Toolbar\toolbar.dll

O3 - Toolbar: &Search Toolbar - {339BB23F-A864-48C0-A59F-29EA915965EC} - C:\PROGRA~1\Toolbar\toolbar.dll

O4 - HKLM\..\Run: [ViewMgr] C:\Program Files\Viewpoint\Viewpoint Manager\ViewMgr.exe
O4 - HKLM\..\Run: [webHancer Survey Companion] "C:\Program Files\webHancer\Programs\whSurvey.exe"
O4 - HKLM\..\Run: [TBPS] C:\PROGRA~1\Toolbar\TBPS.exe

O16 - DPF: {1C78AB3F-A857-482E-80C0-3A1E5238A565} - file://C:\install.cab
iSearch Toolbar
O16 - DPF: {56336BCB-3D8A-11D6-A00B-0050DA18DE71} (RdxIE Class) -
Netster

O18 - Protocol: tpro - {FF76A5DA-6158-4439-99FF-EDC1B3FE100C} - C:\PROGRA~1\Toolbar\toolbar.dll
C:\Program Files\webHancer<----folder

Reboot normally after doing the above, rescan with hijackthis, then post that log here please.

Download, install and keep updated, Spywareblaster from www.javacoolsoftware.com to help keep your system clean.
Reboot into safe mode following the instructions and navigate to and delete the following if found:

C:\Program Files\Viewpoint\Viewpoint Manager<----folder

Thnks Crunchie yeah newdotnet was a very tricky one to get rid of but finally its gone :cool: .. the only thing thats giving me problems is this file
R3 - URLSearchHook: (no name) - {8952A998-1E7E-4716-B23D-3DBE03910972} - (no file)
i fixed it with hijack this in safe mode, but then when i rebooted normally its there in my hijack log....and also theres this "search assistant" file in my add\remove programs, theres no mb specs next to it, is this something i need to get rid of too?thanks..


Logfile of HijackThis v1.98.2
Scan saved at 6:41:31 AM, on 12/19/2004
Platform: Windows XP SP2 (WinNT 5.01.2600)
MSIE: Internet Explorer v6.00 SP2 (6.00.2900.2180)

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\system32\CTHELPER.EXE
C:\Program Files\Grisoft\AVG6\avgcc32.exe
C:\Program Files\Common Files\Real\Update_OB\realsched.exe
C:\PROGRA~1\Grisoft\AVG6\avgserv.exe
C:\WINDOWS\system32\wscntfy.exe
C:\Documents and Settings\julio\My Documents\HJT\HijackThis.exe
C:\WINDOWS\system32\wuauclt.exe

R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
R3 - URLSearchHook: (no name) - {8952A998-1E7E-4716-B23D-3DBE03910972} - (no file)
O2 - BHO: REALBAR - {4E7BD74F-2B8D-469E-C0FF-FD60B590A87D} - C:\PROGRA~1\COMMON~1\Real\Toolbar\realbar.dll
O2 - BHO: (no name) - {53707962-6F74-2D53-2644-206D7942484F} - C:\Program Files\Spybot - Search & Destroy\SDHelper.dll
O3 - Toolbar: REALBAR - {4E7BD74F-2B8D-469E-C0FF-FD60B590A87D} - C:\PROGRA~1\COMMON~1\Real\Toolbar\realbar.dll
O4 - HKLM\..\Run: [CTHelper] CTHELPER.EXE
O4 - HKLM\..\Run: [AVG_CC] C:\Program Files\Grisoft\AVG6\avgcc32.exe /startup
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKLM\..\Run: [TkBellExe] "C:\Program Files\Common Files\Real\Update_OB\realsched.exe" -osboot
O4 - HKLM\..\Run: [eDonkey2000] "C:\Program Files\eDonkey2000\eDonkey2000.exe" -t
O9 - Extra button: AIM - {AC9E2541-2814-11d5-BC6D-00B0D0A1DE45} - C:\Program Files\AIM\aim.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O16 - DPF: DigiChat Applet -
O16 - DPF: {0E5F0222-96B9-11D3-8997-00104BD12D94} (PCPitstop Utility) -
O16 - DPF: {1842B0EE-B597-11D4-8997-00104BD12D94} (iCC Class) -
O16 - DPF: {90C9629E-CD32-11D3-BBFB-00105A1F0D68} (InstallShield International Setup Player) -
O16 - DPF: {FA3662C3-B8E8-11D6-A667-0010B556D978} (IWinAmpActiveX Class) -
See if you can uninstall search assistant from add\remove and if you can't, do the following;

Click Start > Run > Type or copy & paste regedit. The registry editor will open.
Then go to HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall and delete the offending entry in the right hand pane.

It should now be gone from add\remove.

You need to update hijackthis to version 1.99. Run hijackthis & go to Config\Misc Tools\Check for update on-line. If the site is down, go to Remove the old version by opening the program, going to config\misc tools, then uninstall & exit. You then have to delete the file manually. Unzip the new version into the hijackthis folder.

Use the new version to remove these and if you still have problems, try the fix at the end of my post :).

R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName = 
R3 - URLSearchHook: (no name) - {8952A998-1E7E-4716-B23D-3DBE03910972} - (no file)


                                     ---------------------

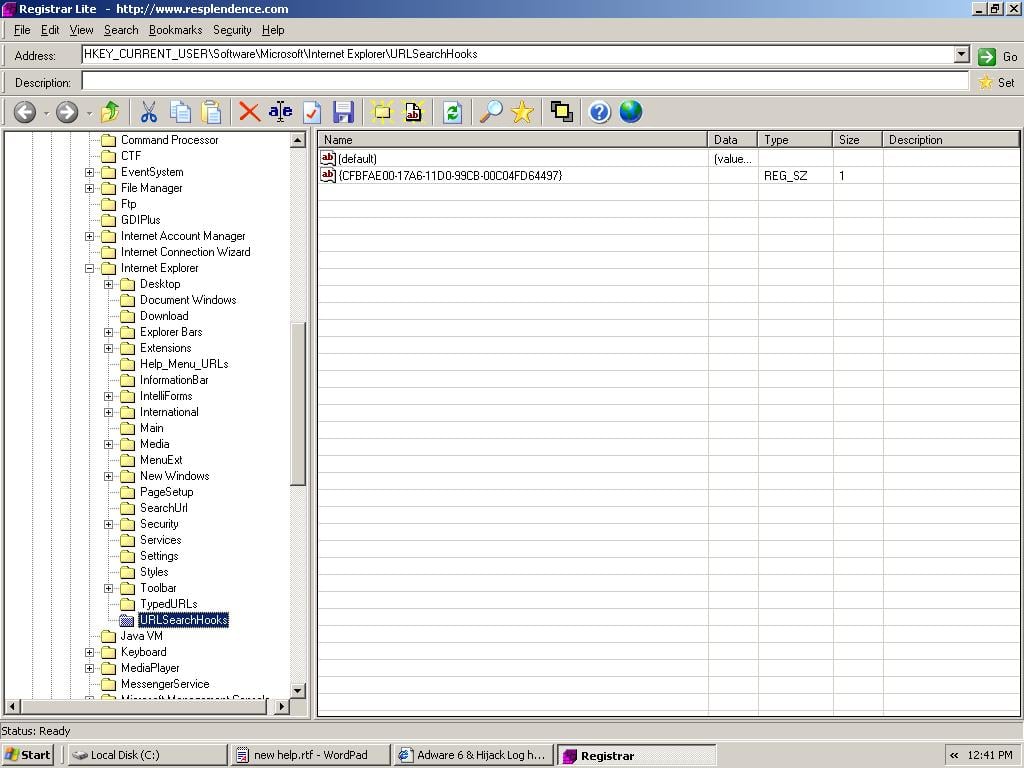
Download Registrar Lite from here: http://www.resplendence.com/download/reglite.exe

Put it in its own folder. You may want to keep this program. It is an excellent free, registry editor.

Copy and paste the follow text into the address bar, then hit 'Go':
HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\URLSearchHooks

In the pane on the right are the values associated with that key.
We want to remove this one>
{8952A998-1E7E-4716-B23D-3DBE03910972}
Right click on it and select delete.
If you get a confirmation question, respond OK then close out of the program.

Cool, heres what ive done so far..

files i got rid off

" search assistant " i removed it from my " add/remove" programs in safe mode.

in Hijack this 1.99
removed
R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
R3 - URLSearchHook: (no name) - {8952A998-1E7E-4716-B23D-3DBE03910972} - (no file)

Viruses that resurfaced
as i was removing the search assistant i saw , then i saw "viewpoint manager (remove only) 0.20mb " in my add/ remove programs..should i remove it , and what does view manager do? cos i have 2 computers ....ones for strictly internet and the other is for music editing .. i rarely dont go on the internet with with my other one but i saw in that " view point file " in my msconfig ..the only thing i do is transferr, mp3s , and some music programs to there .. and i try to scan everything in my old computer before transferring anything there ...shit i hope i didnt catch anythng there...


ok moving on, in the new Hijack This log ive notice it picked up
websearch and wintools (files missing) soo i got rid of half of it ...youll see it on my log..


and this file wasnt in the "regiter lite " file youve mentioned
{8952A998-1E7E-4716-B23D-3DBE03910972}

-------------------Hjack this log---------------------------------
Logfile of HijackThis v1.99.0
Scan saved at 12:31:30 PM, on 12/22/2004
Platform: Windows XP SP2 (WinNT 5.01.2600)
MSIE: Internet Explorer v6.00 SP2 (6.00.2900.2180)

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\system32\CTHELPER.EXE
C:\Program Files\Grisoft\AVG6\avgcc32.exe
C:\Program Files\QuickTime\qttask.exe
C:\Program Files\Common Files\Real\Update_OB\realsched.exe
C:\PROGRA~1\Grisoft\AVG6\avgserv.exe
C:\Documents and Settings\julio\My Documents\hijackthis\HijackThis.exe

O2 - BHO: REALBAR - {4E7BD74F-2B8D-469E-C0FF-FD60B590A87D} - C:\PROGRA~1\COMMON~1\Real\Toolbar\realbar.dll
O2 - BHO: (no name) - {53707962-6F74-2D53-2644-206D7942484F} - C:\Program Files\Spybot - Search & Destroy\SDHelper.dll
O3 - Toolbar: REALBAR - {4E7BD74F-2B8D-469E-C0FF-FD60B590A87D} - C:\PROGRA~1\COMMON~1\Real\Toolbar\realbar.dll
O4 - HKLM\..\Run: [CTHelper] CTHELPER.EXE
O4 - HKLM\..\Run: [AVG_CC] C:\Program Files\Grisoft\AVG6\avgcc32.exe /startup
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKLM\..\Run: [TkBellExe] "C:\Program Files\Common Files\Real\Update_OB\realsched.exe" -osboot
O4 - HKLM\..\Run: [eDonkey2000] "C:\Program Files\eDonkey2000\eDonkey2000.exe" -t
O9 - Extra button: AIM - {AC9E2541-2814-11d5-BC6D-00B0D0A1DE45} - C:\Program Files\AIM\aim.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O16 - DPF: DigiChat Applet -
O16 - DPF: {0E5F0222-96B9-11D3-8997-00104BD12D94} (PCPitstop Utility) -
O16 - DPF: {1842B0EE-B597-11D4-8997-00104BD12D94} (iCC Class) -
O16 - DPF: {90C9629E-CD32-11D3-BBFB-00105A1F0D68} (InstallShield International Setup Player) -
O16 - DPF: {FA3662C3-B8E8-11D6-A667-0010B556D978} (IWinAmpActiveX Class) -
O23 - Service: AVG6 Service - GRISOFT s.r.o - C:\PROGRA~1\Grisoft\AVG6\avgserv.exe
O23 - Service: WebSeach Toolbar support NT service - Unknown - C:\PROGRA~1\Toolbar\TBPSSvc.exe (file missing)
O23 - Service: WinTools for IE service - Unknown - C:\Program Files\Common Files\WinTools\WToolsS.exe (file missing)


:cool: Thnks for helping out man, should i post a hijack log from my other computer here or start a new thread , once this ones clean... i know my new one should be clean cause i rarely go on the internet...

1. Viewpoint Manager: it does, at the very least, "phone home" to check for updates. The program's maker says that you can disable that function through the VM control panel, and also says VM collects no user data or the like.

Care to believe them? ;)

You can safely remove VM if you want. After doing that from the Add/Remove Programs control panel, check to see if a Viewpoint folder still exists on your hard drive; delete it if you find it. Also check your registry for Viewpoint entries and delete those if found.

2. You are using eDonkey, which has adware components. You can opt not to install those components when you install eDonkey, but if you didn't specifically do that, the adware will have been installed automatically.

3.

O23 - Service: WebSeach Toolbar support NT service - Unknown - C:\PROGRA~1\Toolbar\TBPSSvc.exe (file missing)
O23 - Service: WinTools for IE service - Unknown - C:\Program Files\Common Files\WinTools\WToolsS.exe (file missing)

You should delete the entire C:\PROGRAM FILES\Toolbar and C:\Program Files\Common Files\WinTools folders if they still exist.

Be a part of the DaniWeb community

We're a friendly, industry-focused community of developers, IT pros, digital marketers, and technology enthusiasts meeting, networking, learning, and sharing knowledge.