Hi,

I used mysql_real_escape_string to insert a data with apostrophe, in the database, using php.
This works.

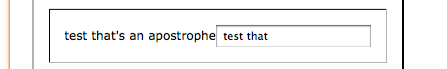
But when I want to select this data and display it in a form's field, it does not work. What happens is that the data before the apostrophe is displayed in the field, but what is after the apostrophe is displayed outside of the field.

Any idea? Does mysql_real_escape_string only work for insert?

Here is my code:

$produpd = $_POST['id-uprod'];

$selectprod=mysql_query("SELECT * FROM products WHERE id='$produpd'");
$selectproda=mysql_fetch_array($selectprod);
$test=mysql_real_escape_string($selectproda[description]);

echo "<table border='2' cellspacing='15' cellpadding='15'>";
			echo "<tr><td>";
			echo "<form action='updatedprod.php' method='post' class='text'>";
			echo "<input type='hidden' name='id-uprod' value='$selectproda[id]' />";
			//echo ($presstext['id']);
			echo "</td></tr><tr><td>";
	        echo "<input type='text' name='name-uprod' value='$selectproda[name_product]' />";
			echo "</td></tr><tr><td>";
			echo "$test";
			echo "<input type='textarea' rows='8' cols='80' name='desc-uprod' value='".mysql_real_escape_string($test)."' />";
			echo "</td></tr><tr><td>";
			echo "<input type='text' name='price-uprod' value='$selectproda[price]' />";

...

Thank you for any help! Please!

Dani AI

Generated

The problem is HTML-escaping, not MySQL escaping. mysql_real_escape_string() protects SQL — it does not make a string safe to put inside an HTML attribute. Placing an unescaped apostrophe inside a single-quoted attribute (or an unescaped quote inside a double-quoted attribute) will break the HTML and truncate the field. Also, <input type="textarea"> is invalid HTML; a textarea is a separate element whose value is the text between its tags.

Building on and : stripslashes/htmlentities touched related symptoms, but the robust fix is to escape for HTML on output and use the correct element. Example approach:

$safeDesc = htmlspecialchars($selectproda['description'], ENT_QUOTES, 'UTF-8');

echo '<textarea name="desc-uprod" rows="8" cols="80">'.$safeDesc.'</textarea>';

echo '<input type="text" name="name-uprod" value="'.htmlspecialchars($selectproda['name_product'], ENT_QUOTES, 'UTF-8').'">';

Notes and troubleshooting:

  • Use ENT_QUOTES so both single and double quotes are encoded (single quote becomes &#039;).
  • Always index arrays with quoted keys ($selectproda['description']) to avoid notices.
  • If the field should render formatted HTML (not be edited as code), output the raw HTML only after sanitizing (XSS risk). If users edit HTML, sanitize on save (libraries such as HTMLPurifier are recommended).
  • Consider migrating from deprecated mysql_* to mysqli or PDO and use prepared statements for DB safety.

These steps will prevent the apostrophe from breaking the form and make the behavior consistent.

Recommended Answers

All 9 Replies

Try this code.

<?
$produpd = $_POST['id-uprod'];

$selectprod=mysql_query("SELECT * FROM products WHERE id='$produpd'");
$selectproda=mysql_fetch_array($selectprod);
$desc= stripslashes($selectproda[description]);

echo "<table border='2' cellspacing='15' cellpadding='15'>";
echo "<tr><td>";
echo "<form action='updatedprod.php' method='post' class='text'>";
echo "<input type='hidden' name='id-uprod' value='$selectproda[id]' />";
//echo ($presstext['id']);
echo "</td></tr><tr><td>";
echo "<input type='text' name='name-uprod' value='$selectproda[name_product]' />";
echo "</td></tr><tr><td>";
echo "$test";
echo "<input type='textarea' rows='8' cols='80' name='desc-uprod' value='".$desc."' />";
echo "</td></tr><tr><td>";
echo "<input type='text' name='price-uprod' value='$selectproda[price]' />";

?>

I think mysql_real_escape_string should be used to just insert data in database not to fetch.

Hi vibhadevit!

Ya I had tried that one too, and I tried again but again what is displayed is only what's before the apostrophe.
Indeed I think you're right, it seems that 'mysql_real_escape_string' only works with insert. But what works with display in a field?

stripslashes displays perfectly outside of the field. But not in a field...

Please help!

just check with data stored in your database and post it here based on that we will make code.

Trial nd error code :

$desc= htmlentities($selectproda[description]);
echo "<input type='textarea' rows='8' cols='80' name='desc-uprod' value='".$desc."' />";

this worked for me.. check at ur end.

Member Avatar for Member #120589

What are you trying to do? mysql_real_escape_string() is a one way procedure. It doesn't need anything when you call it back.

htmlentities() and html_entity_decode(), addslashes and stripslashes work well for non-mysql situations.

Hello,

@ardav: I'm trying to display a data from the database in a form's field.
mysql_real_escape_string() is for inserting

Thank you vibhadevit for your help.

Ok so I will try to not mix anything and explain what I get with what I have.

Here is my field in my database:

This adorable dress is made from a beautiful, soft, textured knit.

<ul>
<li class='text'>Cotton is grown in Pakistan, certified according to <a href="http://www.global-standard.org" target="_blank" class="second">GOTS</a>.</li><li class='text'>Fabric is manufactured in Canada</li><li class='text'>Designs are sewn in Canada.</li>
</ul>

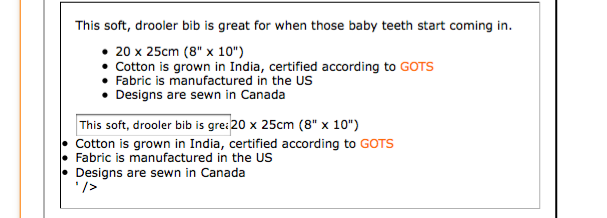
I attached images with the different displays with different function used:
Picture 1: I used:

$desc=htmlentities($selectproda[description]);

and

echo "$desc";
	echo "<input type='textarea' rows='8' cols='80' name='desc-uprod' value='".$desc."' />";

Picture 2:

$desc=stripslashes($selectproda[description]);

and

echo "$desc";
	echo "<input type='textarea' rows='8' cols='80' name='desc-uprod' value='".$desc."' />";

I echo $desc outside of the field to show you that stripslashes works outside of the field, but not inside!

I hope that's enough help for you to figure it out.

Why does htmlentities work for you vibhadevit and not me?

Thank you again...

Info:
the first image that display here is the "Picture 2" that I talk about.
So on this image, the first time the data from the database displays is the first echo, not in a field. And the second time is the echo in the field. The data is in the field until there is an apostrophe or a weird punctuation point I guess.

Member Avatar for Member #120589

OK, so you're trying to export html into a textarea. You shouldn't do this. Place your html into a div - fine, but not a textarea. htmlentities will change '<' into '&lt;', etc. This is meant for displaying code in a div (or similar). Actual code boxes require some heavy validation and security - I don't believe this is what you're looking for.

I was thinking its only about aphostophe.
But you can not show HTML code in textfield.

If you want to edit HTML part, use ckeditor.
If you will use ckeditor editor your problem will be solved.
Check with link if it helps you.

Be a part of the DaniWeb community

We're a friendly, industry-focused community of developers, IT pros, digital marketers, and technology enthusiasts meeting, networking, learning, and sharing knowledge.